Financial services
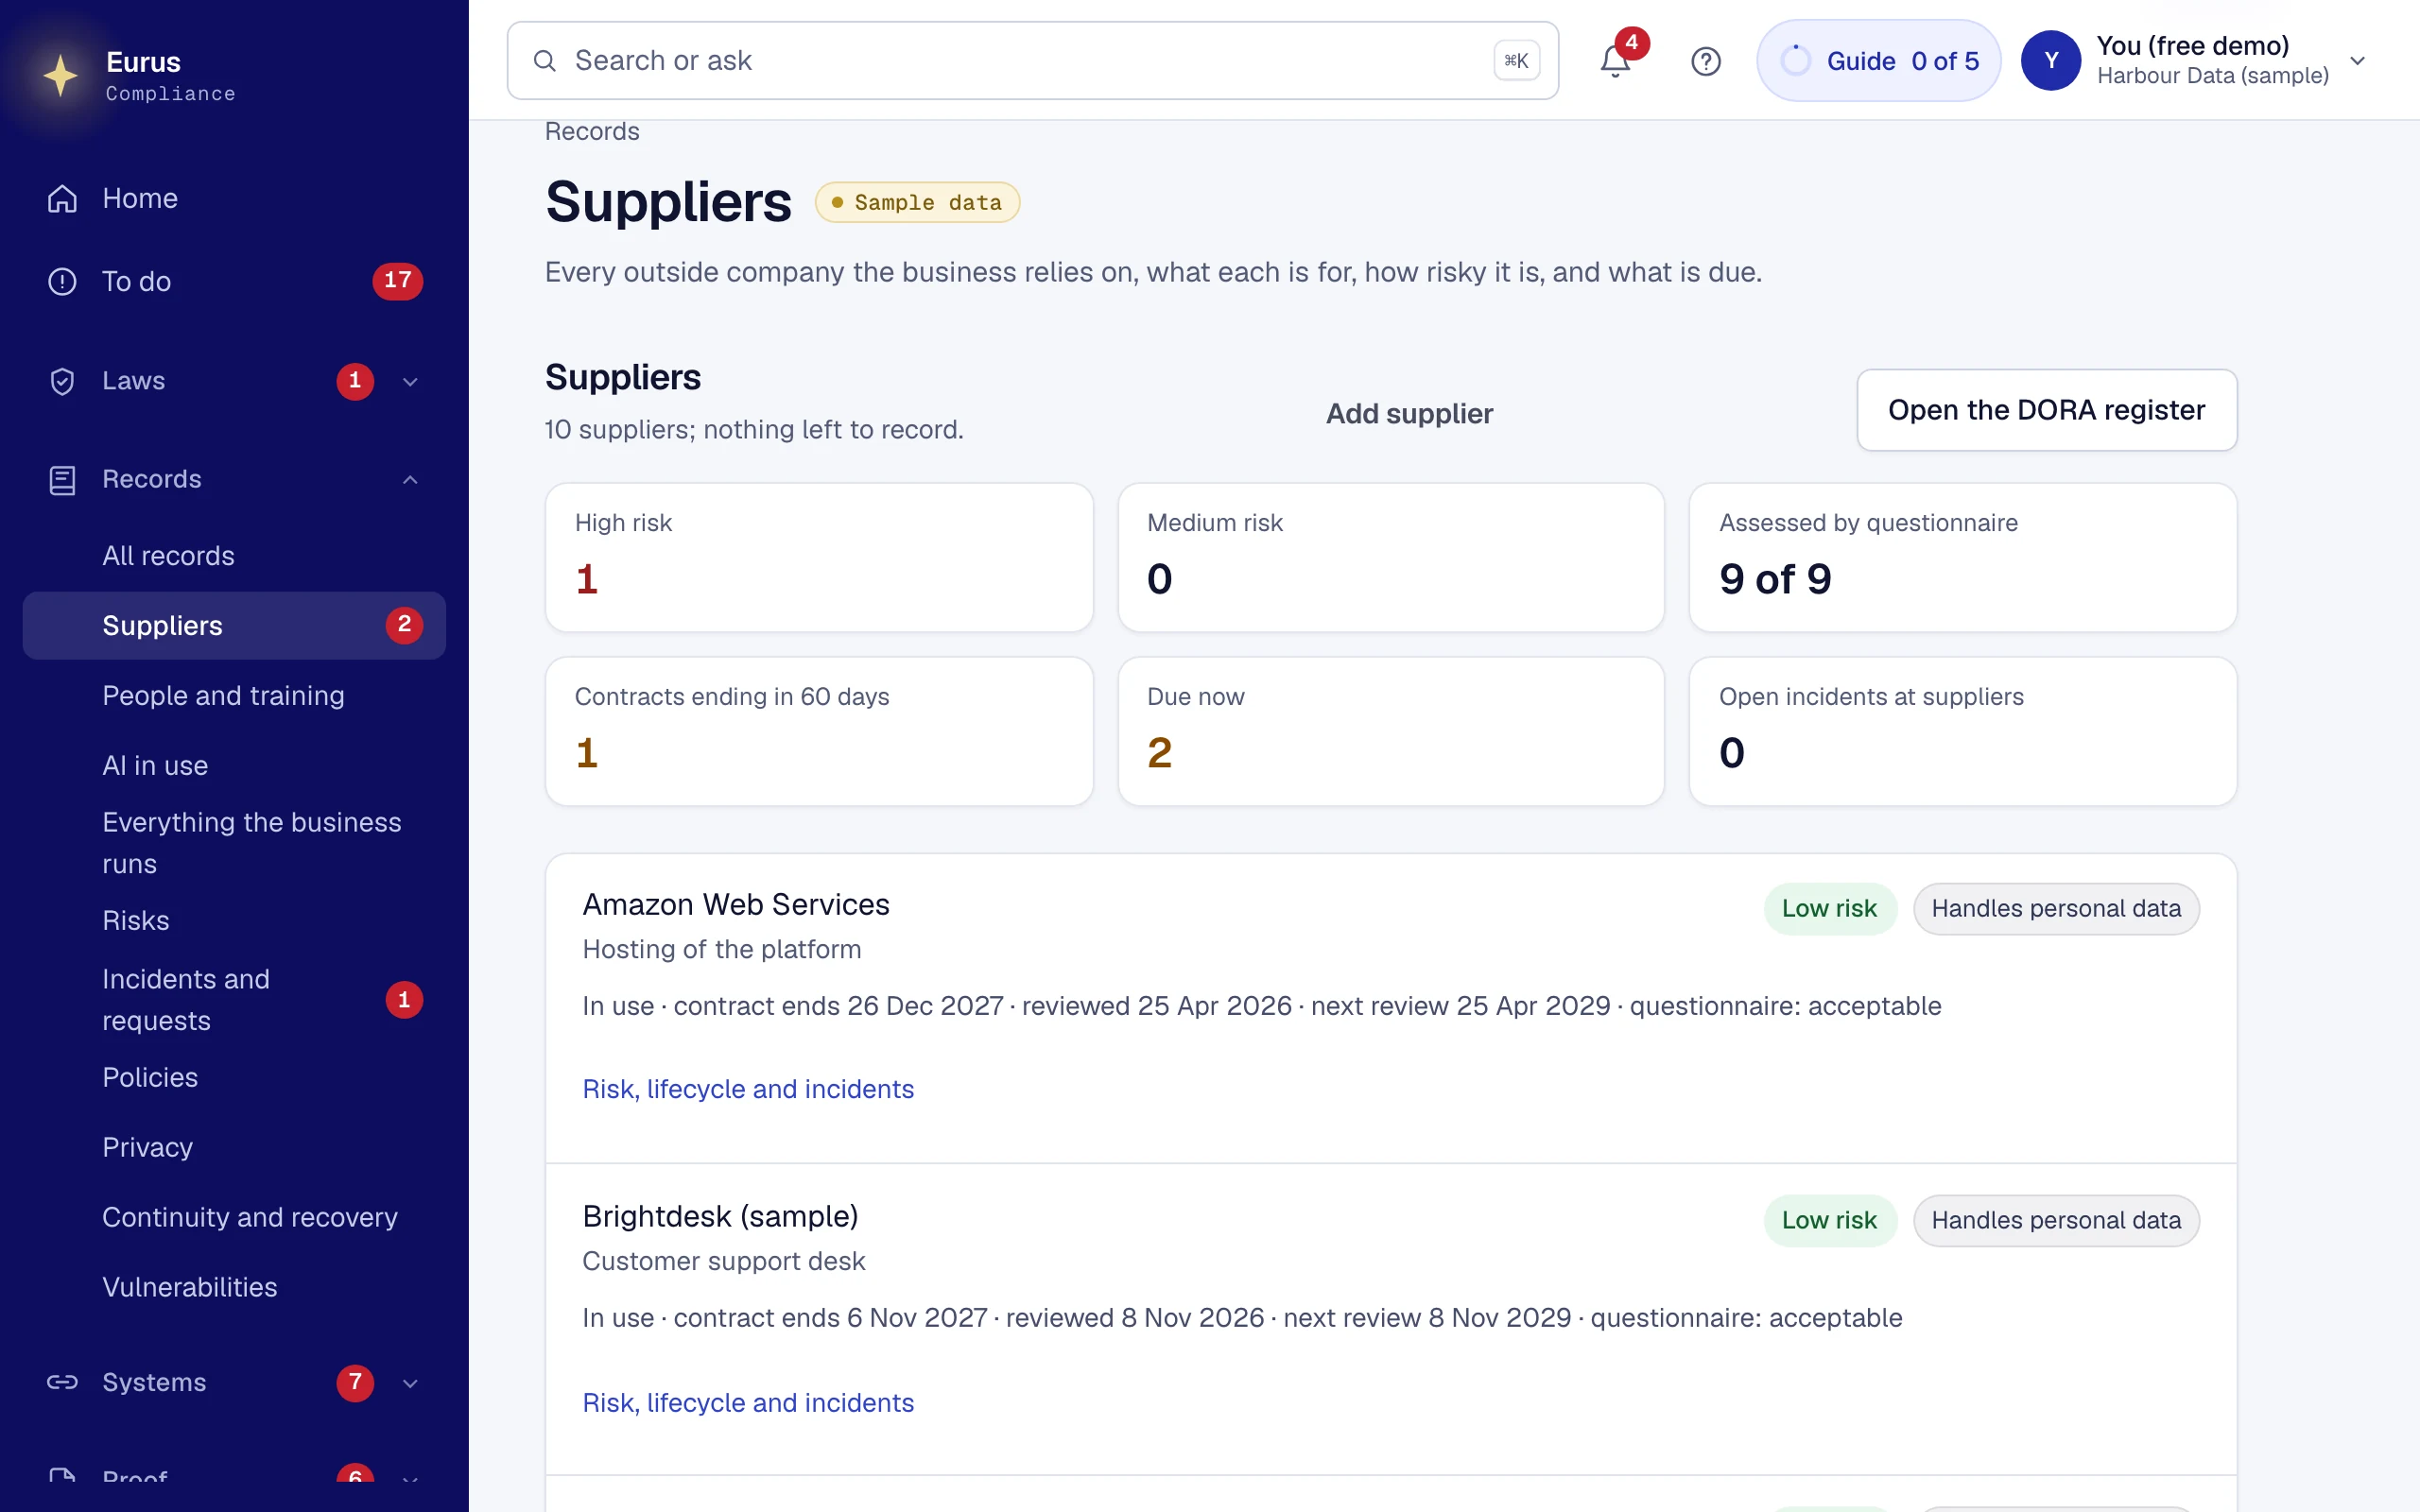
DORA's registers, kept by the systems you run.
Banks, insurers, payment and investment firms answer to DORA, and their technology suppliers answer to them. Eurus keeps the ICT register, the incident clocks and the proof in one record.
What Eurus finds
What Eurus finds in a business like yours.
Connect the systems you already use. Eurus reads them, drafts the registers for a person to confirm, and puts each gap on the To do list with its fix.
- 01
Your ICT suppliers
Each technology supplier found in your systems, drafted for a person to confirm, and kept on the DORA register of information.
- 02
Contracts and reviews
Contracts ending and supplier reviews due, flagged on the To do list before they lapse.
- 03
Incidents and their clocks
An incident starts its clocks as it's recorded: the GDPR's 72 hours, NIS2's 24 and 72 hours, and DORA's 4 hours, side by side.
- 04
Access and leavers
Who can reach what, access reviews signed off each quarter, and leavers' accounts closed.
What it reads
- Sign-in and identity
- Email and calendars
- Files and documents
- Accounts and payments
- HR and people
- CRM and enquiries
- Cloud and code
- Website forms
Which laws apply
Which laws apply, and why.
Eurus works out which of the five apply to your business from what it reads and what you tell it. Here's why each one reaches this sector.
- DORA
Applies to financial entities since 17 January 2025: ICT risk management, incident reporting, testing, and a register of every ICT third-party arrangement.
Regulation (EU) 2022/2554, Articles 5 to 30; register at Article 28(3)
- NIS2
Banking and financial market infrastructures are NIS2 sectors. For financial entities, DORA counts as the sector-specific law, so its rules come first.
Directive (EU) 2022/2555, Article 4 and Annex I; DORA Article 1(2)
- GDPR
Customer and staff data, a record of processing, and a breach notified to the Data Protection Commission within 72 hours.
Regulation (EU) 2016/679, Articles 30 and 33
- EU AI Act
Credit scoring of people, and risk assessment and pricing in life and health insurance, are high-risk uses, with the high-risk rules applying from 2 December 2027.
Regulation (EU) 2024/1689, Annex III point 5, as amended by Regulation (EU) 2026/1744
- ISO 27001
A recognised way for an ICT supplier to show the information security standards DORA expects of it.
ISO/IEC 27001:2022; DORA Article 28(5)
Read more
See Eurus on a sample business.
Try Eurus live first: the full app with a demonstration business, no account needed.